Malware is software designed to cause harm, steal information, disrupt a device, or gain unauthorised access. A virus is one kind of malware. Strange behaviour is a reason to investigate, but it is not a diagnosis by itself.
The labels describe different kinds of harm
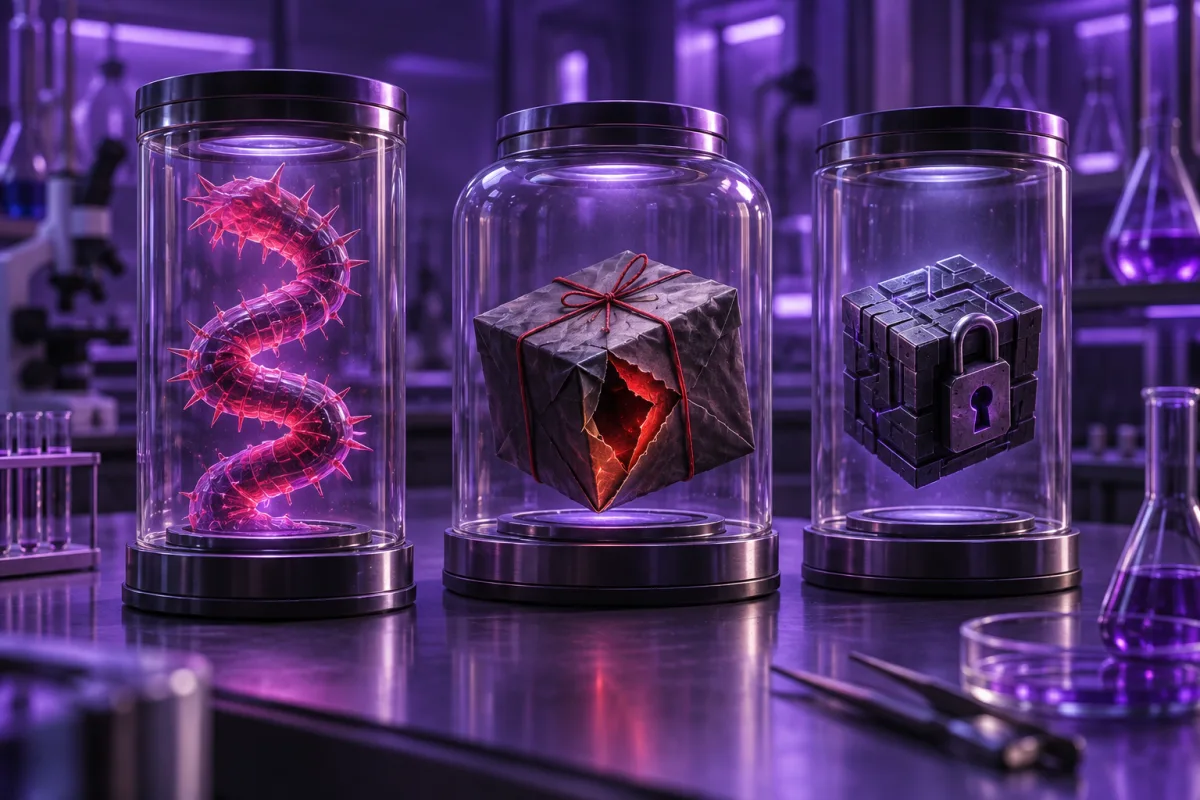
A virus can attach itself to other files and spread when those files run. A worm can propagate through networks. A Trojan is presented as something useful or harmless while performing unwanted actions. These categories can overlap: the important question is what the programme does and how it reached the device.
Ransomware can encrypt files or be used alongside data theft. Spyware collects information without meaningful consent. An information stealer may target passwords, browser sessions, or other account data. Adware and unwanted software can alter browser behaviour, display intrusive content, or install additions you did not intend to use.
How infections commonly begin
A suspicious download is one route, but not the only one. Attackers may exploit unpatched software, abuse an installed remote-access tool, or persuade a user to run a command disguised as a fix. A prompt that tells you to paste instructions into a terminal should receive special scrutiny.
Phishing and malware also intersect. A message may lead directly to credential theft without installing anything, or it may encourage you to open a malicious file. Do not assume that an antivirus warning is the only sign that something went wrong.

Symptoms are clues, not proof
| What you notice | Possible explanations | A useful first check |
|---|---|---|
| Unexpected pop-ups | Site notifications, an extension, unwanted software | Review browser notification permissions and installed extensions |
| High processor use | Updates, indexing, a demanding app, malware | Check the operating system’s process view and recent installations |
| Unfamiliar account activity | Stolen credentials, a shared account, a compromised device | Review sessions from a trusted device and secure the account |
| Files become unreadable | Corruption, storage failure, ransomware | Stop unnecessary writes, disconnect affected systems, and preserve evidence |
What to do if you suspect malware
- Stop entering sensitive information on the device until you understand the problem.
- If active compromise or encryption is suspected, disconnect from networks and shared storage. Contact your IT team for a work device.
- Use another trusted device to secure important accounts if credentials may have been exposed. Change reused passwords and revoke unfamiliar sessions.
- Update legitimate security software and follow its scan or recovery instructions. Preserve the detection names and timestamps.
- Restore only from backups you have reason to trust. For serious or recurring compromise, professional help or a clean operating-system installation may be appropriate.
Prevention is a set of habits
Keep the operating system, browser, and important apps supported and updated. Install software from official distribution routes, use a standard account for ordinary tasks where practical, and be cautious about unsolicited “support” messages. A browser window claiming to have scanned your whole computer is not a trustworthy diagnosis.
Backups deserve their own attention. A backup permanently accessible to an infected device may also be damaged. Keep a separate or versioned copy and test that a small file can be restored. A successful backup notification is not as informative as a successful restore.
Read how to run a useful scan and how to respond to an infection for the next steps.
Questions, answered
Can a Mac get malware?
Yes. macOS has built-in protections, but users and software can still be targeted. Keep the system updated and do not override installation warnings casually.
Does a clean scan prove that I am safe?
No. A scan has a particular scope and point in time. Stolen credentials and account sessions may need separate action even after the device is cleaned.
Sources & further reading
Source review: September 25, 2026. Product features and subscriptions can change; confirm the exact plan before purchase.
About the author
 Oliver ReedDevice & family security
Oliver’s coverage explores device protection, malware prevention, recovery, and family device controls. These guides put operating-system tools first, explain when extra protection may help, and distinguish prevention from a response to an active incident.
View profile and articles