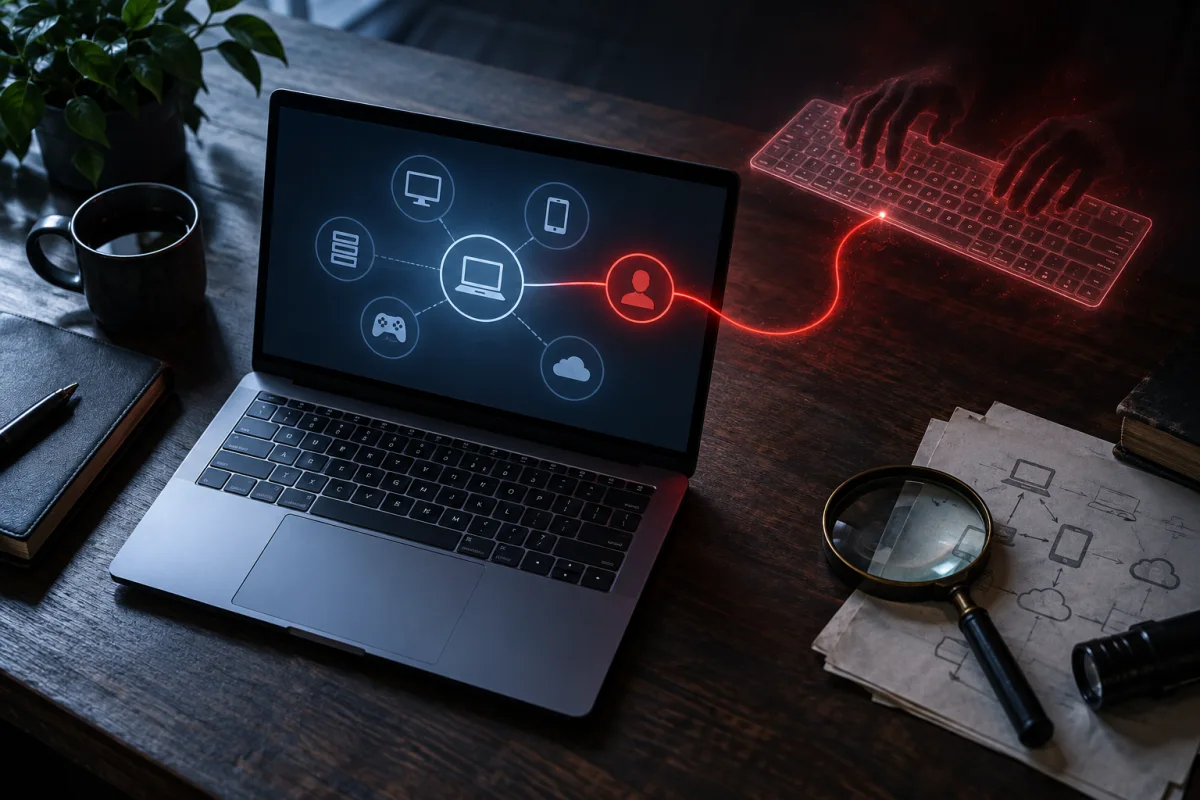
Look for unfamiliar remote-access software, unexpected account sessions, and settings you did not enable. A moving cursor or a slow computer is not conclusive on its own. Preserve evidence and use a trusted device to secure accounts if you suspect compromise.
First distinguish authorised support from a problem
Remote-access software has legitimate uses: workplace support, helping a relative, or managing a computer you own. The risk depends on who can connect, how access is authenticated, and whether that permission should still exist. An old support installation can remain active long after the original session.
If someone unexpectedly calls and asks you to install a support tool, do not use contact details they provide as verification. Contact the organisation through a channel you already trust. A caller knowing your name or describing a common error does not establish that they are authorised.
Start with the applications and settings
- Open the operating system’s installed-app list and review remote-control or unattended-access tools. Do not remove unfamiliar system components simply because their names look technical.
- Inspect startup items and any remote desktop or screen-sharing setting. On a managed device, check with the administrator before changing them.
- Open known remote-access tools and review authorised devices, saved permissions, unattended passwords, and recent sessions where available.
- Remove access you no longer need through the tool’s official controls. Then uninstall unused remote-access software using the normal operating-system method.
Review the accounts around the device
A person may not need remote desktop if they have access to email, cloud storage, or a synced browser account. From a separate trusted device, inspect recent sign-ins, active sessions, recovery methods, and connected apps. Revoke anything you cannot explain.
Change the password for the main email account first if it may have been exposed, because it can often reset other passwords. Use a unique password and strong authentication. If the attacker changed recovery information, follow the provider’s recovery process rather than repeatedly attempting sign-in on a suspect computer.
Preserve clues that make investigation possible
Write down dates, messages, tool names, and account alerts. Screenshots may be useful, but avoid sharing passwords, recovery codes, or private documents in public forums. On an employer-owned system, preserve the state and contact security or IT staff promptly.
If you suspect an active intruder, disconnect the device from the network. This interrupts ordinary remote connectivity but does not remove installed software or secure stolen account credentials. Treat isolation as a first containment step, not the entire fix.
Follow with a device check
Update the operating system and legitimate security software, then run the appropriate scan. Review what the tool finds and whether it quarantines anything. Recurrent detections, unfamiliar administrators, or unexplained remote settings may justify a clean reinstall or professional investigation.
After recovery, re-enable only the access you need. A support session should have a known purpose, a trusted person, and an end. Review unattended access periodically and after changing service providers or disposing of a device.
Questions, answered
Can I identify an attacker from an IP address?
Usually not reliably. Shared networks, VPNs, and proxy services can obscure the person behind a connection. Preserve the information for the appropriate provider or investigator rather than making accusations.
Should I delete every unfamiliar process?
No. Many legitimate system components have unfamiliar names. Verify the publisher and purpose before removing files or disabling services.
Sources & further reading
Source review: September 25, 2026. Product features and subscriptions can change; confirm the exact plan before purchase.
About the author
 Oliver ReedDevice & family security
Oliver’s coverage explores device protection, malware prevention, recovery, and family device controls. These guides put operating-system tools first, explain when extra protection may help, and distinguish prevention from a response to an active incident.
View profile and articles